The Reality of Trying to Bypass Paywall Short Drama Apps
The urge to bypass paywall short drama apps is easy to understand. A series ends on the biggest reveal of the night, the next episode is locked, and a search for “unlimited coins” suddenly produces APK files promising everything for free. The dangerous part is not the missing episode. It is what may be hiding behind that download button.
There is no credible evidence that millions of people download modified short-drama APKs every day, so that claim should not be presented as fact. What we do have are much more useful numbers. Google says Play Protect identified more than 13 million new malicious apps from outside Google Play in 2024, while its 2025 ecosystem report says it blocked 266 million risky installation attempts and protected more than 2.8 billion Android devices with enhanced fraud protection.
Kaspersky’s numbers are equally uncomfortable. Android Trojan-banker attacks increased 56% in 2025, reaching 255,090 unique banker Trojan APK packages, a 271% increase from 2024. In 2024 alone, Kaspersky recorded 1.242 million Android Trojan-banker attacks, up from about 420,000 in 2023.
So the question is no longer simply whether an unofficial app can unlock an episode. The better question is whether saving a few dollars is worth giving an unknown APK access to a phone that may contain banking apps, OTP messages, photos, email accounts and private conversations.
1. Bypass Paywall Short Drama Apps And The Real Attack Surface
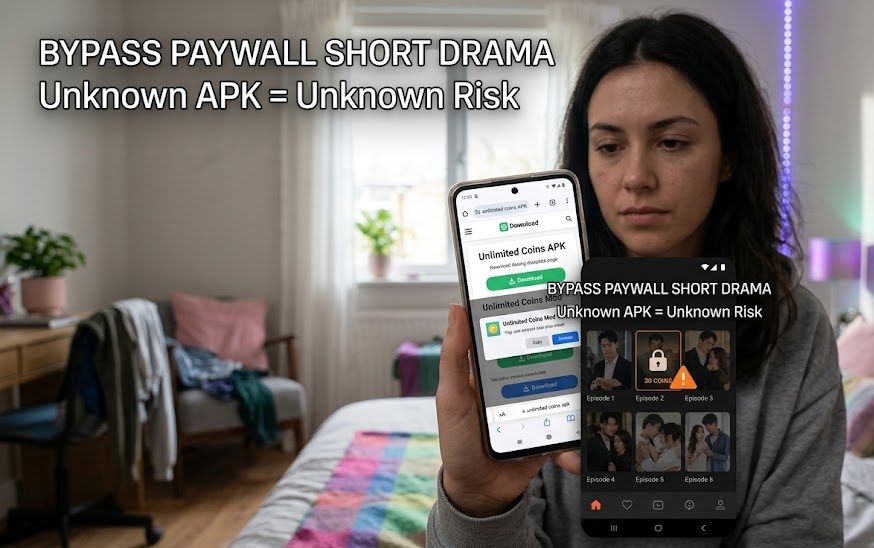
A paywall is normally a business rule. The app checks whether an account has the necessary entitlement, coins or subscription and then allows access.
A modified APK does not automatically rewrite the company’s server.
That distinction matters.
A local modification might change what the interface displays. It does not necessarily change what the remote server considers valid ownership.
This is why claims such as “unlimited coins instantly” should be treated carefully.
Coins are often controlled beyond the phone
Imagine an app displaying:
5,000,000 coins
on a modified interface.
That number can be meaningless if the server maintains the actual account balance.
The server can still determine:
- Account ID
- Coin balance
- Purchase history
- Episode entitlement
- Subscription status
- Device information
- Authentication status
Changing a value stored locally does not automatically change the corresponding server-side record.
This is one reason a supposed coin generator can be more dangerous than useful. The user may believe the software is manipulating the payment system when it is actually manipulating only what appears on the screen.
A fake unlock can be the product
A malicious APK does not need to provide real unlimited coins.
It only needs to convince the victim that it will.
That creates an extremely attractive social-engineering setup:
- Search for a popular drama.
- Find “MOD APK unlimited coins.”
- Download a file.
- Disable a security warning.
- Grant unusual permissions.
- Open the app.
- Discover that something is wrong later.
The attacker has already won the valuable part.
The victim installed their software.
Official terms draw a clear line
ReelShort’s current terms prohibit unauthorized access, attempts to circumvent security features, hacks, cracks, malicious programs and methods intended to modify or disrupt the service. Its terms also state that virtual currency is a limited, revocable license for use inside the service rather than ordinary money that users can freely transfer or manipulate.
That does not prove every unofficial APK is malicious.
It does show that “unlock everything with a modified client” is not the same thing as using an officially supported feature.
2. Mod APK Dangers Become Serious When Banking Data Enters The Picture
The biggest misconception about mod apk dangers is that the worst possible outcome is a banned account.
That is not necessarily the worst outcome.
A malicious application can potentially target data that is worth much more than a few premium episodes.
Kaspersky’s 2025 research found that Android Trojan-banker attacks increased by 56% year over year, while the number of unique Android banker Trojan installation packages reached 255,090, up 271% from 2024. These threats are specifically designed to steal credentials for online banking, electronic payments and card systems.
1. Banking credentials are more valuable than drama coins
A fake short-drama APK might not actually care about your ShortMax, DramaBox or ReelShort account.
It may care about everything else.
Potential targets can include:
- Banking credentials
- Payment information
- OTP messages
- Email accounts
- Social media sessions
- Cryptocurrency wallets
- Contact lists
- Device information
Kaspersky documented a 2025 Zanubis campaign in which malicious APK files disguised as legitimate applications were used to steal banking credentials and digital-wallet keys. The campaign had more than 130 victims in its latest wave and about 1,250 victims since monitoring began.
That is a useful reality check.
The malware does not have to look like “banking malware” to target financial information.
2. Fake entertainment apps can use familiar psychology
An attacker does not necessarily need a sophisticated fake bank interface.
“Unlimited coins” is already a strong hook.
The victim is emotionally motivated to get the next episode.
That makes them more willing to:
- Ignore a Play Protect warning
- Enable installation from an unknown source
- Grant Accessibility access
- Allow notification access
- Permit SMS access
- Turn off security protections
Those permissions are especially important.
Google identifies READ_SMS, RECEIVE_SMS, notification-listener access and Accessibility as sensitive permissions frequently abused in financial fraud.
3. A strange permission is a bigger warning than a strange logo
A fake logo can be copied in seconds.
Permissions are harder to justify.
Ask why a short-drama player needs:
SMS access
or
Accessibility control
or
the ability to read notifications
If the explanation does not make sense, stop.
Google’s enhanced fraud protection specifically looks at these permission patterns when apps are installed through internet-sideloading sources such as browsers, messaging apps and file managers.
3. Cyber Security Risk Is Already Visible In The Sideloading Numbers
The cyber security risk is not theoretical.
Google’s 2024 data found that Play Protect’s real-time scanning identified more than 13 million new malicious apps from outside Google Play. Google also reported that more than 95% of installations associated with major malware families exploiting sensitive permissions and strongly correlated with financial fraud came from internet-sideloading sources such as browsers, messaging apps and file managers.
That 95% figure does not mean 95% of all APKs are malware.
It means that, within Google’s analyzed major fraud-malware families involving those sensitive permissions, internet sideloading was the dominant installation route.
That distinction is important.
Google blocked 266 million risky installation attempts in 2025
Google’s 2025 ecosystem report gives another useful number.
In 2025, enhanced fraud protection:
- Covered more than 2.8 billion Android devices
- Expanded to 185 markets
- Blocked 266 million risky installation attempts
- Helped protect users from 872,000 unique high-risk applications
Google also said it prevented more than 1.75 million policy-violating apps from being published on Google Play and banned more than 80,000 bad developer accounts attempting to publish harmful apps.
Those numbers explain why turning off Play Protect to install an “unlimited coins” APK is such a bad trade.
You would be deliberately removing one of the defenses designed to identify exactly this category of risk.
Android is becoming stricter about unknown APKs
Google announced additional developer-verification measures for certified Android devices.
For Indonesia, the new verified-developer requirements are scheduled to take effect in September 2026. Google says apps installed on certified Android devices in the affected regions will need to be registered by verified developers.
That does not mean every sideloaded app is malicious.
It does mean the Android ecosystem is moving toward stronger accountability for software distributed outside traditional app stores.
4. Fake Coin Generators Are Usually The Wrong Thing To Trust
The phrase fake coin generators sounds almost harmless.
It is not.
A website claiming:
“Enter your username → choose 999,999 coins → verify human → download APK”
is a classic red-flag pattern.
The “human verification” may be the actual monetization mechanism.
The verification step can be the trap
A fake generator may ask the user to:
- Install another application.
- Complete a survey.
- Enter personal information.
- Allow browser notifications.
- Download another APK.
- Share the page.
- Complete multiple offers.
The promised coins never arrive.
The website earns money from the user’s activity.
Community reports around short-drama coin “hacks” have described this exact pattern, with users reporting that supposed verification links redirected them through surveys or repeated downloads rather than producing coins. These are anecdotal reports, not proof that every generator is fraudulent, but they illustrate a recurring pattern worth recognizing.
A real generator would still face the server problem
Suppose you type:
Username: Mila
Coins: 999,999
The website can generate that number visually.
It cannot simply assume that ShortMax, DramaBox or another service will accept the number as legitimate account credit.
The remote service controls its own database.
That is why screenshots of “successful” generators prove very little.
Never enter credentials into a coin website
This rule is simple.
If a third-party generator asks for:
- Email password
- Google password
- Apple ID
- Banking information
- OTP
- Recovery code
- Cryptocurrency seed phrase
leave immediately.
No short drama episode is worth that information.
5. Illegal Streaming Truth And Why The “Free Episode” May Cost More
The illegal streaming truth is less glamorous than the promise.
Pirated streams and modified apps often remove the payment layer by replacing it with a different business model.
Someone still needs to make money.
That may happen through:
- Advertising
- Redirects
- Affiliate downloads
- Data collection
- Subscription traps
- Fake verification
- Malware
- Credential theft
Not every unofficial website uses every technique, and not every pirate site is automatically malware.
But the user loses an important advantage: accountability.
With an official app, there is a known developer, a store listing, terms, update mechanism and a route for reporting abuse.
With a random APK mirror, those protections may be absent.
The “free” price can become a security bill
Consider a hypothetical example.
A user wants to avoid paying $10 for a short-drama subscription.
They install an unofficial APK.
The APK steals an email session.
The attacker then accesses a shopping account.
A saved payment method is exposed.
The original $10 saving suddenly becomes irrelevant.
The exact financial loss will vary by incident, but the principle is straightforward: the value of the data on the phone can be dramatically higher than the price of the content being bypassed.
Short dramas are not worth disabling security
This is where the risk-benefit calculation becomes easy.
| Choice | Immediate benefit | Main downside |
| Official free episodes | No extra payment | May have ads or limits |
| Official subscription | Convenient access | Recurring cost |
| Official coin purchase | Immediate unlock | Can become expensive |
| Random MOD APK | Promised free access | Malware and account risk |
| Fake coin generator | Promised unlimited coins | Phishing, redirects or fake verification |
| Pirated stream | Potentially free | Legal, privacy and security uncertainty |
The safest options are boring.
That is precisely why they work.
6. What To Do If You Already Installed A Suspicious Short Drama APK
If you have already installed one, do not panic.
Do not immediately start deleting random files either.
Follow a controlled response.
1. Disconnect first if the app is behaving suspiciously
If you notice unexpected pop-ups, strange accessibility behavior, unknown SMS activity, overheating, unexplained battery drain or unusual banking notifications, disconnect the phone from the internet while you assess the situation.
If banking activity looks suspicious, contact your bank using its official channel.
2. Remove suspicious permissions
Review the app’s permissions.
Pay special attention to:
- Accessibility
- SMS
- Notifications
- Contacts
- Microphone
- Camera
- Device administration
Google specifically highlights SMS, notification and Accessibility permissions as high-risk when abused by malicious apps downloaded through internet-sideloading routes.
3. Uninstall the unofficial app
Do not keep it installed simply because “nothing has happened yet.”
Malware does not need to reveal its purpose immediately.
Some threats wait for particular conditions before activating.
4. Run Google Play Protect
Keep Play Protect enabled.
Google says Play Protect continuously scans Android applications and has expanded real-time defenses against malware and fraud.
If the phone shows a warning, take it seriously.
Do not search for a tutorial telling you how to disable the warning.
5. Change important passwords from a clean device
If the suspicious APK had access to sensitive information, prioritize:
- Primary email
- Google or Apple account
- Banking accounts
- Payment services
- Social media
- Password manager
Use a different trusted device where possible.
Enable two-factor authentication.
If banking credentials or OTPs may have been exposed, contact the bank rather than waiting for an unauthorized transaction.
6. Check account activity
Look for:
- Unknown logins
- New devices
- Password changes
- New recovery emails
- Unexpected transactions
- New payment methods
- Unfamiliar app permissions
The earlier you notice suspicious activity, the easier it is to contain.
The Safer Way To Get More Short Drama Without Hacking Anything
The safest solution is not complicated.
Use the official app.
Take the free episodes.
Watch legitimate ads when available.
Collect officially offered rewards.
Compare the total cost of coins with the subscription.
Then decide whether the ending is worth paying for.
If the cost is too high, stop watching or wait for an official promotion.
For viewers comparing subscription economics, a breakdown such as the DramaBox subscription value guide is more useful than downloading an unknown “unlimited coins” file because the decision stays focused on price and viewing habits rather than device security.
The short-drama business model may be frustrating.
Paywalls can be aggressive.
Coin systems can be confusing.
Cliffhangers can be brutal.
But none of those problems justify handing an unknown APK access to a phone containing your financial life.
The numbers tell the bigger story.
13 million new malicious apps identified outside Google Play in 2024.
266 million risky installation attempts blocked in 2025.
872,000 unique high-risk applications covered by Google’s enhanced fraud protection.
56% growth in Android Trojan-banker attacks during 2025.
255,090 unique Android banker Trojan installation packages in 2025.
Those figures do not prove that a particular short-drama MOD APK is malicious.
They prove something more useful: the threat environment is large enough that installing unknown software for the sake of free entertainment is a poor gamble.
If a short drama asks you to pay, you have three sensible choices.
Pay through the official system.
Use the legitimate free options.
Or leave the episode locked.
The one option that deserves far more skepticism is the file promising that someone has magically made the entire paywall disappear.
Q&A
Can a modified APK really give unlimited short drama coins?
It may alter what the app displays locally, but that does not prove the remote service has accepted a new coin balance. Server-side entitlements and account balances are controlled by the platform. A screenshot showing millions of coins is therefore not evidence of a legitimate server-side credit.
Does every Mod APK contain a banking Trojan?
No. That claim would be too broad. A modified APK can be harmless, broken, ad-injected, privacy-invasive or malicious. The problem is that users generally cannot establish the security of an unofficial build simply from the promise “MOD unlocked.” Google’s and Kaspersky’s data show why internet-sideloading and Android malware deserve serious caution.
What is the first thing to do after installing a suspicious APK?
If there are signs of compromise, disconnect the device, remove suspicious permissions and uninstall the application, then run Play Protect. If banking credentials, OTPs or financial information may have been exposed, contact the relevant bank or payment provider and change important account credentials from a trusted device.

Leave a Reply